I spun up a fresh Debian VPS, grabbed the public IP, and before I’d even finished setting up my shell aliases I ran journalctl -u ssh out of curiosity. Thousands of failed auth attempts already. Not after a week, not after a day — within minutes of the box existing on the internet, automated botnets were already hammering port 22 with dictionary passwords. That’s not a hypothetical threat model. That’s the default state of a cloud server the moment it gets an IP.
Cloud providers hand you compute. They don’t hand you security — that part’s entirely on you, and the gap between “default install” and “actually hardened” is bigger than most people assume until they watch the logs.
Where the Defaults Actually Fail #
| Vector | Default state | Hardened state | Risk |
|---|---|---|---|
| Root access | PermitRootLogin yes |
PermitRootLogin no |
Critical |
| Auth method | Password-based | Key-only (ed25519) | Critical |
| Firewall | Unmanaged, all ports | Default-deny incoming (UFW) | High |
| Brute force | No rate limiting | Automated IP banning (Fail2ban) | High |
| Patching | Manual | Automated security updates | Medium |
Step 1: Stop Using Root Directly #
Root for daily admin work is a bad habit that gets expensive the first time something you’re running gets compromised — if that process is running as root, whoever exploited it now owns the whole machine, not just the app.
ssh root@your_server_ip
adduser deploy
usermod -aG sudo deploy
Swap deploy for whatever username you actually want — the point is just that it isn’t root.
Step 2: Kill Password Auth Entirely #
Passwords get brute-forced, phished, reused across breached sites. An ed25519 key isn’t vulnerable to any of that the same way — it’s asymmetric math, not a string someone can guess or leak from some unrelated service.
Generate the key locally, not on the server:
ssh-keygen -t ed25519 -C "admin@example.com"
ssh-copy-id deploy@your_server_ip
Then log in as your new user and lock down the daemon itself:
sudo nano /etc/ssh/sshd_configPermitRootLogin no
PasswordAuthentication no
PubkeyAuthentication yes
PermitEmptyPasswords no
X11Forwarding no
MaxAuthTries 3
AllowUsers deployBefore you restart anything, validate the syntax in a separate terminal from your active session — one typo here and you can lock yourself out entirely with no way back in except console access through your hosting provider:
sudo sshd -t
sudo systemctl restart ssh
Open a brand-new terminal, try logging in with ssh deploy@your_server_ip. If it’s configured right, no password prompt appears at all — you’re in on the key alone.
Step 3: Build a Real Firewall Perimeter #
Debian ships with nothing actively filtering incoming traffic by default. Every port is reachable unless something explicitly blocks it.
sudo apt update && sudo apt install ufw -y

sudo ufw default deny incoming
sudo ufw default allow outgoing

sudo ufw allow 22/tcp
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp

sudo ufw enable
sudo ufw status verbose
Deny-by-default means anything you haven’t explicitly opened stays closed, which is the posture you actually want on a public-facing box — open only what you know you need, nothing more.
Step 4: Fail2ban for the Attempts You Can’t Fully Block #
Password auth being off doesn’t stop bots from hammering SSH anyway — it just means they’re wasting their own time instead of actually getting in. Still, that traffic eats log space and system resources for nothing, so you ban it outright.
sudo apt install fail2ban -y
sudo nano /etc/fail2ban/jail.local
Create the override file rather than editing the package defaults directly — package updates will stomp anything you put straight into the default config files.
[DEFAULT]
bantime = 86400
findtime = 600
maxretry = 3
banaction = ufw

[sshd]
enabled = true
port = ssh
logpath = %(sshd_log)s
backend = systemd
Three failed attempts inside a ten-minute window gets an IP banned for a full 24 hours. backend = systemd tells Fail2ban to read straight from the journal instead of parsing flat log files, which is both faster and matches how modern Debian actually logs by default.
sudo systemctl enable --now fail2ban
sudo fail2ban-client status sshd
Step 5: Automate the Patches You’ll Otherwise Forget #
Manual patching means your server falls behind the moment you get busy with something else, and security patches don’t wait for your schedule.
sudo apt install unattended-upgrades -y
sudo dpkg-reconfigure -plow unattended-upgrades
Say yes when it asks about enabling daily automatic updates. Here’s where a lot of guides get the wrong key — it’s easy to assume Debian and Ubuntu share this setting since they’re related, but they don’t. Ubuntu uses Allowed-Origins; Debian uses Origins-Pattern, and the pattern syntax itself is different too. Check /etc/apt/apt.conf.d/50unattended-upgrades and make sure it actually reads like this:
Unattended-Upgrade::Origins-Pattern {
    "origin=Debian,codename=${distro_codename},label=Debian-Security";
    "origin=Debian,codename=${distro_codename}-security,label=Debian-Security";
};
Write Allowed-Origins into that file on a Debian box instead, and it just gets silently ignored — the package still installs, the service still runs, and you walk away thinking you’re covered when nothing’s actually being filtered by that rule at all. That’s worse than an obvious error, because nothing tells you it failed.
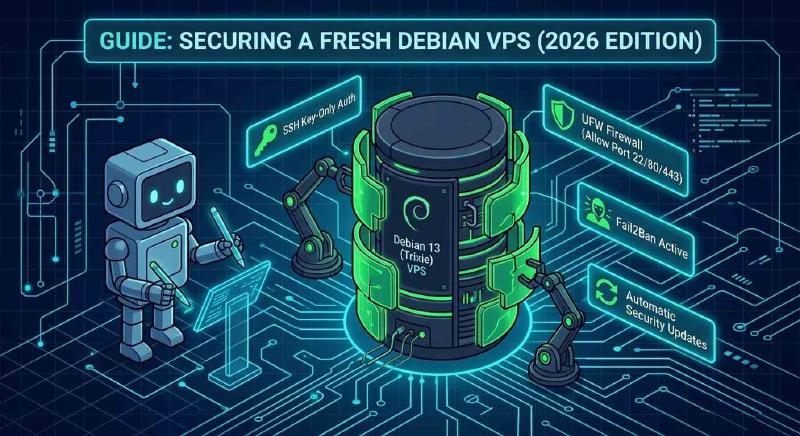
Five pieces, and none of them optional on anything facing the public internet: lock out root, kill passwords, default-deny the firewall, ban the brute-force noise automatically, and patch without having to remember to. Skip any one of them and you’re relying on luck instead of a security posture — and based on that log output from minute one, luck runs out fast.